CheckEmoji Community · the emoji forum
🏠 Home 🆕 What's new ❓ Unanswered 🔥 Popular 📡 RSS Members 👥 0 online log in · register
Home › Miscellaneous › Forum Help! › Has there been a security breach on the forum?

Has there been a security breach on the forum?

Started by Megan Thomas5 · · 👁 10 views · 49 replies

📡 Subscribe to replies

Participants Megan Thomas5Alexander Diaz4coppersailor28Jessica Morris6Casey BennettGeorge Cook31Jack Cook7wearybison63Bradley White73urbanheron4Jose Miller3mistybisoncrimsonhound80silentviper8Matthew Jackson2
Casey Bennett Casey Bennett Regular
522 messages
joined Nov 2011
#21 ·
Linda King said:It’s high time someone told Anderlon that he needs to step up and lead his people toward a new frontier. 🕺 He needs to let go of that fear; we’re all standing right behind him, and we aren't backing down until this whole thing is finished. 👍

LMAO. There’s always one guy leading the charge, running ahead of the pack while waving a flag like he owns the damn place. 😁
George Cook31 George Cook31 Newcomer
6 messages
joined Oct 2021
#22 ·
Casey Bennett said:I mean, if someone was actually that obsessed with reading forum DMs, they’d probably just target specific people they found interesting instead. It would be way more low-key that way.
And honestly, nobody would even realize they’d been hacked unless there were those crazy messages left in their signature.

Yeah, you've got a point there. I guess I really don't have any clue what actually drives hackers to do what they do. 😵

As far as my email goes, I actually set up a dedicated one just for this forum, so if things ever go sideways, it wouldn't really be a huge deal.
And I'm pretty sure I can trust that getting my forum profile back won't be too much of a headache. 🙂
Casey Bennett Casey Bennett Regular
522 messages
joined Nov 2011
#23 ·
So far, we haven't seen any instances where someone actually had their email or password changed within the forum database.
God forbid that ever happens—if you find yourself locked out of your own profile and unable to trigger a password reset, just create a clone account and reach out via a direct message or hit us up on the help desk. We’ll run a quick verification check and get your original profile restored.
It shouldn't be an issue. We have dealt with people before who haven't logged in for ages, lost access to their registered email, or simply forgot their credentials... those situations get resolved.

However, it's clear the hackers aren't interested in hijacking accounts; they're strictly after spamming. Why they bother doing it is beyond me. I suppose they just want to push our buttons.
Casey Bennett Casey Bennett Regular
522 messages
joined Nov 2011
#24 ·
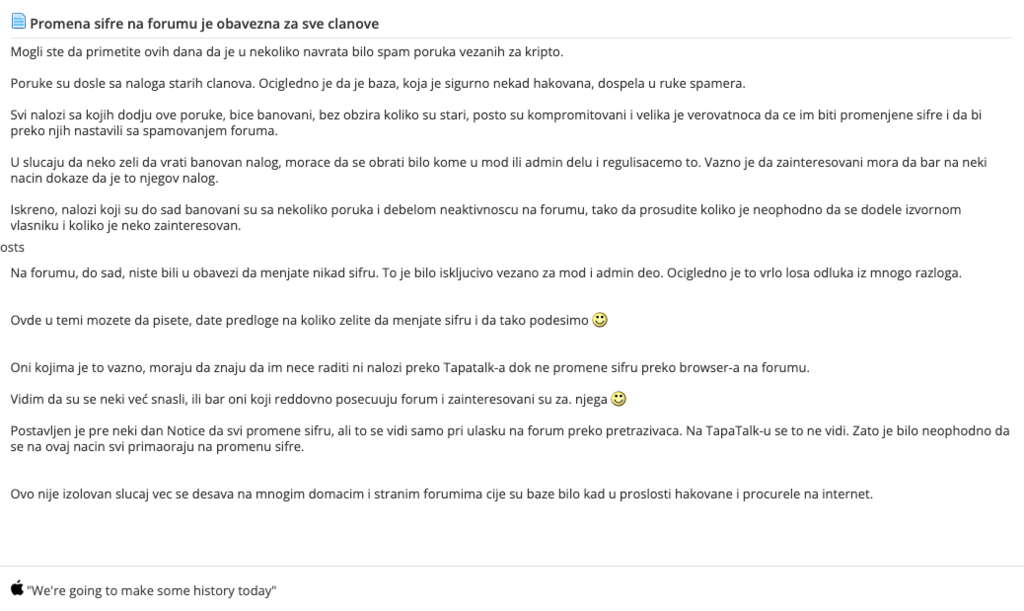
Found this notice over on that other local forum.

I know I posted an image that’s way too large—it's practically unreadable otherwise.

image
Jack Cook7 Jack Cook7 Regular
376 messages
joined Aug 2017
#25 ·
Yo, restless crew!

The guy trying to "brute force" passwords clearly isn't out for blood, since he's actually flagging bad passwords right here on the forum. If you ask me, he’s just messing around with some ancient accounts. We can debate his motives all day if we want.

And yeah, it's just me, Leclerc—not some massive security breach called Jack Cook7.
coppersailor28 coppersailor28 Active Member
156 messages
joined Mar 2012
#26 ·
For easier reading—processed via optical character recognition tools

(@Casey Bennett, you can swap out your profile picture and just delete this post of mine)

Password updates are mandatory for all members

You likely noticed an uptick in crypto-related spam over the last few days.

The messages are coming from long-standing accounts. It’s clear our database was
compromised at some point and is now in the hands of spammers.

Any account posting these messages will be sent to the
ban corner, regardless of account age.
They are compromised, and there's a high probability their passwords have been hijacked
to facilitate further spamming.

If someone needs to recover a banned account, they must contact the mod or admin team to resolve it.
The user will need to provide sufficient proof of ownership.

To be blunt, the accounts banned so far have been largely inactive with minimal post history.
Use your judgment regarding how much effort we put into returning them to the original owners.

Until now, password changes weren't required here. That was strictly reserved for mods and admins.
Clearly, that was a poor decision.

You can use this thread to offer suggestions on the frequency of required updates
so we can set the parameters accordingly. 🙂

For those concerned: note that accounts won't work through
Tapatalk until the password has been updated via a standard web browser.

Some users have already handled this—specifically those who frequent the forum regularly
and actually care about it. 🙂

A news notice was posted a few days ago regarding the mandate, but it only appears
when logging in via a browser. It doesn't show up on Tapatalk. This thread is necessary
to ensure everyone is forced to comply.

This isn't an isolated incident. It happens constantly on many American and international forums
where databases were leaked online following past hacks.
Jessica Morris6 Jessica Morris6 Active Member
195 messages
joined Nov 2022
#27 ·
Jack Cook7 said:Hey there, you skeptics out there.

The guy behind this whole "password stuffing" thing doesn't seem to have any malicious intent, honestly, because the forum itself is flagging incorrect passwords immediately. As far as I can tell, he’s just messing around with some ancient accounts... we can debate his motives if we want, but that's my take.

And yeah, just for the record, it's me, Leclerc, not some security breach called Jack Cook7.

He's probably just trying to farm clicks. I recall him promoting some crypto group on Telegram where they apparently share investment tips or something similar...
Jack Cook7 Jack Cook7 Regular
376 messages
joined Aug 2017
#28 ·
Mark Cruz15 said:He’s probably just trying to farm clicks for some quick cash. I recall him shilling some crypto group on Telegram where they supposedly drop investment tips.

So, basically, this guy thinks he can just spam clicks until he gets shut down by the mods? Like, what's the end game there?

Man, why was I born with such a massive brain and an even bigger appetite for clickbait?
Give me some decent teeth and clear vision instead, honestly.
Jessica Morris6 Jessica Morris6 Active Member
195 messages
joined Nov 2022
#29 ·
Jack Cook7 said:So, basically, someone’s out here trying to farm clicks just to harass a forum that's bound to push back pretty quickly?

Good grief, why wasn't I born with a massive bank account and a mountain of clout instead...
And maybe a few more healthy teeth and better eyesight while I'm at it.

Everything's going to be fine, just don't let it get to you.
Jose Miller3 Jose Miller3 Regular
446 messages
joined Mar 2024
#30 ·
Jack Cook7 said:If you ask me, he’s just messing around with some ancient accounts... we can argue about his motives all day if we want.

Not all of them are old, though.

Case in point—I literally just deleted a thread and banned an account where the last post was back in January of '23. 🤷

Most of them are old, sure, but they aren't *all* old... some of these were clearly made recently and used immediately 🤷
...
mistybison mistybison Regular
495 messages
joined Aug 2008
#31 ·
Is there any way to secure my profile against potential hacking attempts?

I’ve noticed over in the ban corner that even active members who haven't logged in for a while are having their accounts compromised.

Since I haven't had much free time to check the forum lately, I want to make sure I don't log back in one day only to find my account banned and a bunch of junk posted under my username.😁
Jack Cook7 Jack Cook7 Regular
376 messages
joined Aug 2017
#32 ·
Rachel Brooks63 said:Not all of them are ancient history.

So, I actually just nuked a thread and banned an account where the last activity was way back in January '23. 🤷

Most of those accounts are oldies, but not all—some are totally fresh accounts just made for this specific purpose. 🤷

It’s super likely they’re just cycling through random accounts, hitting dozens or even hundreds at once by testing basic "easy" passwords from a dictionary. Since there’s usually a limit on failed login attempts, the script is probably rigged to dodge that by using long timeouts between tries while simultaneously moving on to the next account.

That’s basically how you track down which logins got hit.

mistybison said:Is there any way to protect my profile from getting hacked?

I see in the ban corner that even active members who haven't logged on for a bit are getting their profiles hijacked.

Since I haven't had much time to hang out on the forum lately, I really don't want to show up one day only to find my profile banned and a bunch of garbage posted under my name. 😁

Go with a password that's at least 8 characters long, mix in uppercase and lowercase letters, some numbers, and other stuff like ! , # , = or -
George Cook31 George Cook31 Newcomer
6 messages
joined Oct 2021
#33 ·
Jack Cook7 said:The password needs to be at least 8 characters long, using a mix of uppercase and lowercase letters, some numbers, and maybe a few special symbols like ! or # or even an equals sign or a dash.

Honestly, if I had to use a password like that, I probably wouldn't even be able to log in myself after a day or two. 😵
Jack Cook7 Jack Cook7 Regular
376 messages
joined Aug 2017
#34 ·
George Cook31 said:Honestly, with a password like that, I wouldn't even recognize myself trying to log in. 😵

Check this out:

Dog<>Cat!
Jessica Morris6 Jessica Morris6 Active Member
195 messages
joined Nov 2022
#35 ·
mistybison said:Is there actually any way to truly lock down a profile against potential hacking, or are we all just sitting ducks waiting for someone to find a backdoor...

I was just browsing through the ban corner, and honestly, it looks like things are getting pretty messy... apparently, they’re even hacking into the profiles of active members who haven't even been hanging around the forum for a while...

I haven't really had much time to hang out on the forums lately, and I honestly wouldn't want to log in one day only to find my profile banned and a massive pile of garbage written under my name... 😁

Just change your password and update your email address... I honestly think that should be enough to fix the situation.
crimsonhound80 crimsonhound80 Active Member
175 messages
joined Mar 2008
#36 ·
Mark Cruz15 said:Just swap out your password and change your email address—honestly, I think that covers just about everything.

Look, trying to brute-force its way into someone's profile using a password like 4r%Zi9$"Gr... is basically impossible.
It's all just campfire stories.
The only real way someone gets in is if they manage to hijack the actual email account you used to register for this forum... then we're talking about Trojans or some other ridiculous malware nonsense that uncovers all your saved credentials and such...

Don't sweat it, lady... @mistybison/">@@mistybison 😉
silentviper8 silentviper8 Newcomer
3 messages
joined Jun 2021
#37 ·
crimsonhound80 said:Breaking into someone’s profile using a password like 4r%Zi9$"Gr.. is basically impossible.
It’s just fairy tales.
The only real risk is if someone gets hold of the email you used to register for this forum... then they hit you with a Trojan or some other nonsense to scrape all your passwords.

Don't sweat it... @mistybison/">@@mistybison 😉

Passwords get pulled straight from an SQL database.☕ You could have the most complex password on the planet and still get hacked.

I think Tapatalk is down, since most of us use it anyway.🐔
Jack Cook7 Jack Cook7 Regular
376 messages
joined Aug 2017
#38 ·
silentviper8 said:Passwords get pulled straight from the SQL database ☕ you could pick the most insane, complex password on the planet and still get hacked

Not exactly, though. Passwords aren't just sitting in the database in plain text; they're hashed using stuff like MD5 or SHA1/128/256/whatever else.

So, even if you somehow get your hands on the password database, you wouldn't be able to log in using those "passwords." That's literally what hashing is for.

I think Tapatalk went down, since basically everyone on the forums uses it. 🐔
mistybison mistybison Regular
495 messages
joined Aug 2008
#39 ·
Jack Cook7 said:Use a password that is at least 8 characters long, featuring a mix of uppercase and lowercase letters, numbers, and special symbols like !, #, = or -.

All of my passwords look like long strings of random characters and numbers, making them nearly impossible to memorize on my own. 😁

I will certainly include some special characters next time I update my credentials. 🤔 😁

On a side note, the forum keeps logging me out whenever I try to post a comment. 😁
silentviper8 silentviper8 Newcomer
3 messages
joined Jun 2021
#40 ·
Jack Cook7 said:Not really, because passwords aren't stored in the database in their original form; they’re hashed using MD5, SHA1, or whatever else.

So, even if you get access to a password database, a kid isn't going to be able to log in with those "passwords." That's the whole point of hashing.

SQL injection is an old-school hacking method, but it still works quite well on legacy web apps. I know, because I've used it myself. ☕

Nowadays, people lean more toward mobile apps for hacking—either by pushing out some free app that everyone downloads just to run a keylogger, or by targeting a popular mobile app to scrape user data.

A hash isn't impossible to decrypt; it just takes time. 🙂

You must log in or register to reply here.

Log in Register

🔗 Similar threads