CheckEmoji Community · the emoji forum
🏠 Home 🆕 What's new ❓ Unanswered 🔥 Popular 📡 RSS Members 👥 0 online log in · register
Home › Jack Cook7 › Posts

Posts by Jack Cook7

796 posts shown.

Has there been a security breach on the forum? in Forum Help! ·
Someone’s running this super slow script just to test out everyone's forum passwords. It’s designed to be incredibly gradual so it flies right under the radar of the provider's IDS/IPS systems—since those things mostly just flag the aggressive, loud attacks.

The guy behind it is actually decent enough that every single time he cracks a password, he leaves the exact same message.

I honestly don't know what his real endgame is, though I can take a pretty good guess.
Has there been a security breach on the forum? in Forum Help! ·
Can I jump in here for a sec?
urbanheron4 said:Just set it to 4096, though honestly, it doesn't even matter. It'll probably just pick 4096 by default anyway. That number basically tells the drive how big its clusters are in bytes. So, if you save a tiny little file under 4 KB, it’s gonna hog the full 4 KB because that's the minimum chunk size. If you drop a 7 KB file on there, it eats up 8 KB (two clusters). That's why you always see that weird gap between the actual file size and the "size on disk."

Not quite.

Look, setting aside all the specific OS jargon, a cluster is really just a collection of "atomic"—you know, indivisible—units, or whatever they decide to call them in a specific file system. Some folks just call them "blocks."

A block is a single unit on the drive, whereas a cluster is basically just a bunch of those blocks scattered around.

Basically, a block is a group of consecutive logical "sectors." With Fat, the logical sector is 512 bytes. For NTFS, it's 4096.

Then you have the logical sector mapping to a "physical" one, which can range from about 512 bytes up to maybe 4096 bytes plus a little extra for ECC.

And get this: one "physical" sector might actually be mapped to anywhere from one to eight actual physical sectors on an HDD, especially when you've got four disks working in parallel (that's 8 surfaces!).

When you're dealing with RAID controllers or smaller storage arrays, there's at least one more layer of mapping involved (called a chunk), and with the massive enterprise stuff? There are way more layers than that.

In the real world, a tiny 12-byte file (like just the text Hello World) could end up eating through a few megabytes of actual physical space.

Super simple once it clicks.
Network security key in IT Support ·
John Cook72 said:the password on the router sticker isn't encrypted at all

Not exactly.
Abolishing partial credit in Feedback & Suggestions ·
Kareem Abdul-Jabbar, why are you even letting them do this to you?
Network security key in IT Support ·
The whole point of a password is that it’s encrypted.

There’s this massive 75-hour "Security" course over on Khan Academy that basically teaches you everything there is to know.
Abolishing partial credit in Feedback & Suggestions ·
briskdrifter3, why are you even putting yourself through this, begging them to let you off the hook from their random-ass decisions?
Network security key in IT Support ·
Since people have been jumping you for about ten years now, I’d say watch your back. This crowd can get pretty brutal.
Network security key in IT Support ·
Paul Rogers94 said:back when I was using a dial-up modem—way before I lost the password

Anyone who ever hopped on my modem back when I actually knew the password is probably still auto-connecting whenever they get close enough to pick up my router signal.

This laptop has been sniffing out signals from random offices and coffee shops all over New York City, so it’s definitely set to hunt for Wi-Fi—I just need that damn password.

Hopefully, I can figure it out tomorrow when someone stops by. If I can use their phone or their Wifia to snag the password like you described above, we'll be golden.

A QR code pops up on my end that anyone can just scan with their phone if they want to jump on my network.

Man, it sounds like anyone who walks by your place can just hijack your internet whenever they feel like it, and honestly, that's a massive security risk.

Fix that ASAP tomorrow. If you can't, just shut the whole thing down until you get it sorted.
Network security key in IT Support ·
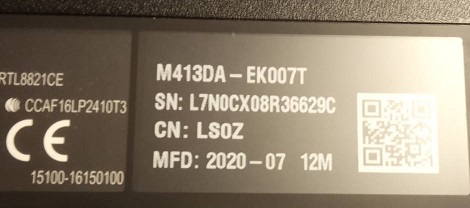
Paul Rogers94 said:this part is on my bottom side

image

Alright, looks like you've got an M413DA, which is a Dell.
https://www.dell.com/laptops/for-stu...m413/techspec/

And get this—there’s zero ethernet port here. Just Wi-Fi 5 and Wi-Fi 6. (!!!)
Wi-Fi 5(802.11ac) (Dual band) 1*1 + Bluetooth® 4.1
Wi-Fi 6(802.11ax) (Dual band) 2*2 + Bluetooth 5
Wi-Fi 5(802.11ac) (Dual band) 2*2 + Bluetooth® 4.2

So basically, you can't just plug a cable from the laptop straight into the router. You're stuck using wireless.

That means you'll need to know all those connection settings, which brings us back to checking your phone.

How exactly are you connecting via Wifia?
Network security key in IT Support ·
Paul Rogers94 said:I've got some buddies coming over tomorrow who connect to my PC, so I'll check if they can get this option working on their phones too.

Thanks a ton, man. Everything you're saying makes total sense, I’m just being a bit slow on the uptake here.

Look, you aren't stupid. You just haven't mastered this specific tech yet. No biggie.

By the way, if you have an "English keyboard" without those extra American characters, you can actually grab some letter decals and just stick them on yourself. You can get black or white letters depending on what color background you're working with.
https://www.homedepot.com/b/hardware-adhesive-lettering/N-5yc1vZ

Oh, and don't forget to hit the letters with some clear nail polish once they're stuck on—it'll make them last way longer before they start peeling.
Network security key in IT Support ·
Paul Rogers94 said:I know how to plug a cable into a laptop, but there isn't an actual port for it

I'm not sure if it matters, but the laptop was bought overseas, so it's got a US keyboard layout

Oof.🤦

Some laptops just don't come with an Ethernet RJ45 port. What exact model are you rocking? Grab the Part Number (P/N)—it's usually slapped on the bottom somewhere.
Network security key in IT Support ·
Paul Rogers94 said:8

Alright, so you're looking at an Ethernet cable with an RJ45 connector. Here’s what the end of a Cat5e cable looks like:
https://www.cmple.com/content/images...ID0007843.jpeg

Just plug one end into the Ethernet port on your laptop and the other into a port on your router—look for something labeled LAN1. Heads up though, some ports on those routers are usually set aside for phone lines, typically LAN3 or LAN4, so steer clear of those.

Give it about 10 seconds to settle, then fire up your browser and try hitting a site like www.cnn.com
Network security key in IT Support ·
Paul Rogers94 said:So, if I plug my laptop straight into the router using a cable, will it just grab all the important settings automatically and then work fine over Wi-Fi later?

thanks man

now I'm even more frustrated 🙂

My phone just shows me some QR code for the Wi-Fi, and the ethernet cable won't fit into my laptop because it's too thin—does it need some different kind of port?

Alright, let's tackle the cable issue first. That's the easier win.

Take a look at both ends of the cable. How many copper pins/contacts are on those plugs—is it 2, 4, 6, or 8?
Network security key in IT Support ·
Paul Rogers94 said:so does that mean

1. if I plug my laptop straight into the router with an Ethernet cable, it'll grab all the important settings automatically?

2. and then later on, I can just use the Wi-Fi normally?

1. Yeah. (Pretty much.)

2. Nope. You gotta set up the Wi-Fi separately since there are extra parameters involved. We'll tackle that once you get the main issue (1) sorted out.

where am I supposed to find this DHCP client?

thanks man

The DHCP client service is built into every single Windows install. It’s basically running by default even if you aren't touching it. Just plug the laptop into the router via Ethernet, give the machine a quick reboot to let everything settle, and you should be good to go—you'll be able to hop on a browser and hit a site like Reddit or whatever.

Then we'll move on to the next step.
Network security key in IT Support ·
Paul Rogers94 said:That sticker fell off me, and I tucked it away somewhere but now I can't find it for the life of me

So, I just picked up a new laptop and I'm stuck—how do I get it online without knowing the password?

Is there any way to track it down?

Maybe through my phone since it's already connected?

Look, you’ve basically got two different things to worry about on your router:

1.a) The default login/password used to actually log into the router's settings via an Ethernet cable (like if you wanted to change stuff from your desktop)
1.b) And/or just getting out to the internet (which usually doesn't require a login once you're connected; it just works)

2. The login/password specifically for joining the Wi-Fi network to get internet access; usually, you aren't even allowed to mess with the router settings once you're just on the Wi-Fi side.

That sticker on the bottom typically only gives you the info for (1.a). Some brands don't even have stickers, but you can always just Google the user manual to find the factory default admin login/pass.

From what I can tell, you're looking for (2). If you want that laptop browsing the web over Wi-Fi, and you've already got a phone connected to the router's Wi-Fi, just jump into your phone's Wi-Fi settings, toggle "show password," and then just type those same details into your laptop. Easy peasy.

If you're trying to plug the laptop directly into the router with an Ethernet cable, you shouldn't even need a password. Just make sure your laptop is set to grab an IP automatically (DHCP), and it should pull everything it needs right when it boots up.

Either way, you're gonna eventually need to figure out both the admin login for the hardware and the Wi-Fi password to actually surf the web.
Old PC: Best wiping methods before recycling? in IT Support ·
Quote : How to Use DoD 5220.22-M
analogfox63 said:Hi there,
Could someone point me in the right direction on how to completely wipe everything from an old computer before I toss it out?

So, I was just thinking about that whole US DoD thing again. You know, when people start talking about high-level security standards? It’s always that massive US Department of Defense benchmark. Honestly, it sounds way more intimidating than it actually is once you get into the weeds of it, but man, it carries some serious weight!
So, I was just falling down a rabbit hole reading about data security, specifically that whole deep-clean process people talk about when they’re getting rid of an old hard drive. It brings up this massive question: Windows have you heard of DoD? Seriously, if you've ever thought about selling your laptop or just tossing an old one, you need to know about this. There's this specific standard—Quote : How to Use DoD 5220.22-M—that basically tells you how to make sure your files aren't just "hidden," but actually gone. Like, vanished into thin air. We aren't just talking about hitting "delete" and emptying the trash bin. That's amateur hour! If you want to be safe, you're looking at the US Department of Defense document #5220.22-M. It’s the gold standard for a reason. The gist of it? You use specific wiping methods : Fill sectors with zero to overwrite everything. It's like taking a marker and scribbling over a notebook until you can't see the lines anymore. It’s thorough, it’s intense, and honestly, it’s kind of satisfying to think about. I saw analogfox63 mentioning something similar the other day, and it got me thinking—most of us probably don't need full-blown military-grade scrubbing for a family photo collection, but hey, better safe than sorry, right? Especially if you're running a Windows PC with sensitive stuff on it. Whether you're on Windows 11 or still rocking an old Windows 7 setup, the principle stays the same. Don't leave your digital life lying around for some random person to find!
So, you want to scrub a hard drive clean? Like, *really* clean? If you're looking to wipe a drive on a Windows PC using that heavy-duty standard, you’re probably talking about Quote : How to Use DoD 5220.22-M. It sounds super intense and official—which, let's be honest, it is—but it basically means you aren't just hitting "delete" and hoping for the best. You're actually overwriting the data so it stays gone. If you're running Windows 11/10/8.1/8/7 / Vista, you can't just rely on the basic format tool if you want to follow the rules. You need specific wiping methods : Fill sectors with zero to make sure those old files don't just pop back up like uninvited guests at a BBQ. I was chatting with analogfox63 about this the other day, and they were asking if this stuff is overkill for a home user. Honestly? Maybe. But if you've got sensitive info on there, better safe than sorry! It's kind of like a classic Worf-like approach to data security—total annihilation of the target. No survivors. If you're trying to get this done on an Enterprise machine or even just a standard Windows PC, you'll likely need some third-party software that specifically supports the DoD 5220.22-M protocol. Just search for tools that mention the US Department of Defense document #5220.22-M and you'll find what you need. Umm, one quick heads-up though: once you pull this trigger, there is NO going back. It's permanent. So, double-check that you've backed up anything you actually care about before you start the wipe. Trust me, I've seen people regret it! Got questions? Check out the FAQs in most of these wiping tools. They usually walk you through the whole process step-by-step. Good luck!
Ever stumbled upon the whole DoD wiping thing and felt totally lost? Like, yeah, I've heard the term, but what does it actually *mean* for my data? If you're staring at those technical specs feeling a bit overwhelmed, you should definitely give this article a deep dive. It breaks everything down so you can finally wrap your head around it and grab a pro-grade DoD wipe tool that actually gets the job done.

So, I've been spiraling down this rabbit hole lately about data security—specifically that whole DoD wiping method thing. You know, when you're trying to make sure your old tech isn't basically a giant "please hack me" sign for anyone walking by? I was looking into the Quote : How to Use DoD 5220.22-M stuff, and man, it gets deep. It’s not just hitting "delete" and calling it a day. We aren't talking about a simple trash bin cleanup here; we're talking serious business. If you're running a Windows PC and you want to be absolutely certain your files are gone for good, you have to look at the actual wiping methods : Fill sectors with zero. That's the heavy-duty stuff. It reminds me of how people used to talk about those old-school cleaning rituals, almost like a classic Worf-like level of discipline. You can't just be half-hearted about it if you want total peace of mind! Anyway, I'm still digging through the technicalities of the US Department of Defense document #5220.22-M to see how it actually applies to a standard home setup versus something massive like an Enterprise environment. Does anyone else get obsessed with this kind of niche security stuff, or is it just me?
So, let's talk about DoD 5220.22-M. This whole thing is basically a data sanitization method that first popped up in the US Department of Defense document #5220.22-M. Basically, it’s a specific way to overwrite those old-school hard disk drives (HDDs) using nothing but patterns of ones and zeros to make sure everything is wiped clean. If you want to dive deeper into how this DoD disk wipe works, check out these FAQs:

So, everyone keeps asking me this one: how many passes are we actually talking about when people mention a DoD wipe? It's funny because there’s always that debate in the forums. Some folks think you need to scrub a drive until the end of time, while others are all like, "Just do it once and call it a day!" If you're looking at the actual US Department of Defense document #5220.22-M, the standard usually points toward three passes. But honestly, if you're just trying to clear out an old Windows PC before selling it on eBay, sometimes even a single pass of overwriting is plenty. It really depends on how paranoid you're feeling! Are we talking about sensitive government data or just some old family photos and spreadsheets? Huge difference. Anyway, I've seen people go overboard with these crazy multi-pass wipes that take forever, and then you see someone else just delete everything and think they're safe. Neither extreme is quite right. If you want to be sure, stick to the basics. What do you guys think? Are you a "three-pass minimum" kind of person, or do you just wipe it once and move on with your life?

So, here's the deal with that DoD standard—it’s basically a three-pass wiping method. What it actually does is overwrite every single addressable spot on your hard drive using a specific sequence: first, it hits everything with binary zeros, then it goes back through with binary ones, and finally, it finishes off with a random bit pattern for that third pass. Simple enough, right?

So, about that DoD 5220.22-M stuff... if you're looking at the ECE—which is basically just the beefed-up, extended version of DoD 5220.22-M—we're talking a full 7-pass method. Yeah, seven! Talk about overkill, right?

So, I've been getting this question pop up a lot lately, and honestly, it’s a bit of a toss-up. Like, how long does a DoD wipe actually take? It really depends on what kind of gear you're working with. If you're running an old-school Windows PC with a spinning hard drive, prepare to grab a coffee—or maybe a whole meal. We're talking hours, sometimes even a full day if you're dealing with a massive drive. But if you've moved over to an SSD? Things change. The math basically boils down to the size of your drive and the speed of your connection. A bigger drive means more sectors to hit during those wiping methods : Fill sectors with zero, which obviously drags things out. It's a waiting game, plain and simple.

Honestly, it all boils down to how much space you're working with on that hard drive. It’s a huge factor. Plus, don't forget that the interface type can totally mess with your wiping speed, too. It really makes a difference!

Can you actually get your data back once it's been hit with a DoD wipe?

Look, if you go the route of a DoD wipe, you're basically setting that data in stone. It’s going to shut down pretty much every software-based recovery trick out there, and honestly? It’ll even block most—if not all—of those intense hardware-based recovery attempts people use to scavenge info off a drive. Once it's done, it's done.

So, I’ve been seeing this question pop up a lot lately, and honestly, it’s worth a deep dive. Can you actually use the DoD 5220.22-M standard to wipe an SSD? Short answer: It’s... complicated. Like, "trying to use a sledgehammer to fix a watch" complicated. See, that whole DoD 5220.22-M protocol was basically designed back when we were all rocking spinning hard drives. Back then, if you wanted to make sure data was gone, you just overwrote those magnetic sectors with zeros or random bits over and over again. Simple, right? But SSDs don't play by those rules. They use something called wear leveling, which moves data around constantly to keep the drive from burning out. If you try to run a traditional multi-pass wipe on an SSD, you might think you're hitting every sector, but the drive's controller is essentially playing hide-and-seek with your data behind the scenes. You could finish the wipe and still have traces of your files sitting in "retired" cells that the software can't even see. Plus, doing multiple passes like that is a total drag on the lifespan of your drive. You're basically putting unnecessary mileage on it for nothing. If you really need to sanitize an SSD, you shouldn't be looking at old-school overwriting methods. Instead, look into the "Secure Erase" command built into the drive itself, or use manufacturer-specific tools. That triggers a hardware-level reset that clears the cells much more effectively than any software-based DoD method ever could. Anyway, just my two cents! Don't go wrecking your hardware thinking you're being extra secure.

Look, don't go trying to use DoD standards to wipe an SSD. Seriously, don't do it. An SSD just doesn't work like an old-school HDD—the whole architecture is totally different. If you actually want to scrub your data and sleep easy at night, you need to learn how to properly erase an SSD securely right here.

If you're looking to scrub an old HDD or a thumb drive clean, you've gotta do it right. I'm talking about that deep-clean level where nothing is left behind for some hacker to find. I've been digging through some stuff lately, and honestly, if you want to follow the gold standard, you should be looking at Quote : How to Use DoD 5220.22-M. It’s basically the manual everyone points to when they want to make sure data is gone for good. When people talk about wiping methods : Fill sectors with zero, they're usually trying to hit that sweet spot of security without spending ten hours waiting for a progress bar. If you're on a Windows PC running Windows 11 or even an older setup like Windows 7, there are plenty of ways to trigger this. I remember talking to analogfox63 about this once—they were super worried about leaving traces on an old laptop. And yeah, I get it! It's better to be safe than sorry. Whether you're dealing with a massive Enterprise drive or just a tiny USB stick you found in your desk, using a method based on the US Department of Defense document #5220.22-M is the way to go. Just a heads up: don't go thinking a simple "delete" button does anything. That's like sweeping dust under a rug instead of actually vacuuming. You want that total wipeout. Any specific tools you guys are leaning towards? Let me know!
If you’re looking to pull off a proper DoD secure erase on a hard drive, you’re gonna need a rock-solid disk wipe tool in your arsenal—I’m talking about AOMEI Backupper Professional. Honestly, it’s a lifesaver. You get a ton of killer features out of it that make the whole process way smoother:

You’ve got four different ways to go about it: wiping methods : Fill sectors with zero, filling them with random junk, the DoD 5220.22-M standard, or even the heavy-duty Gutmann method. It basically covers all your bases depending on how much security you actually need!
It’s actually super handy because you aren't just stuck wiping HDDs—you can totally use it on USB sticks and SD cards too!
It basically lets you whip up some bootable media so you can run a full-on bootable disk wipe. Super handy!
It doesn't matter what kind of setup you're running—this works on pretty much any Windows PC out there. We’re talking full support for everything from the brand-new Windows 11 down to the old-school Windows 10, 8.1, 8, 7, Vista, and even that ancient XP. If it runs Windows, you're good to go!
Feeling adventurous? Go ahead and grab the best DoD wipe software for your Windows PC right now. Give it a shot!

If you want to be 100% sure? Like, totally, absolutely certain? Just physically destroy the media. I’m talking shredding your HDDs, SSDs, USB sticks, CDs... all of it. Then, take those scraps and burn them. Boom. Done.
Chris Rogers2 said:I couldn't find anything useful in the app texts or logs besides total transmitted packets, overhead, and stuff like that, so I just grabbed a Wireshark capture of some gameplay. Ping was steady at 42-43.

Basically, most of the packets (UDP) range from 57 bytes on the wire (15 bytes of data) to 72 bytes on the wire (30 bytes of data), making up about 70% of the traffic. Then, from 73 bytes on the wire (31 data) up to 212 on the wire (170 data), that’s another 20%. The remaining 10% are the outliers, ranging from 218 on the wire (176 data) up to 789 on the wire (747 data).

The absolute max I captured was 909 bytes on the wire, which is 867 bytes of data.

Sent you the log via DM.

Whoops, turns out 100M is actually a bit much for me...🙂

Anyway, you've basically done all the heavy lifting with the analysis already. The real takeaway here is that gaming UDP packets are tiny. Most frames—whether they're running over local Ethernet or some LTE/broadband connection—are basically empty shells, which means huge overhead (even if WAN frames aren't strictly fixed lengths). Even the biggest UDP packet stays within that 1432-byte end-to-end limit, so we aren't dealing with any fragmentation issues.

What we're still guessing at is whether those UDP packets are splitting across both links during edge cases. If they are, you might run into resequencing headaches, but honestly, the game's own TCP/IP stack usually handles that. Typically, if you're pushing UDP over LTE but receiving it over broadband, you'll get hit with a massive RTT difference between the two paths. The big question is: is the router shifting the entire connection/UDP port XX over to LTE, or is it just dumping the "extra" traffic onto LTE? We just don't know.

Then you've got IPTV streaming (and VoIP), which wants the exact opposite—bigger, jumbo frames. On decent layer 2+ manageable gear, Ethernet usually lets you push 8K to 9K packets, and high-end switches or routers can even handle up to 64K.

So, theoretically, you could tweak the settings on your PC to drop the Ethernet frame size from the standard 1512 down to something like 1024, and crank the TV up to 8192 to boost performance for both.

But man, we're back to square one: you don't have root access to the router. You can optimize things locally all you want, but it doesn't mean squat once the frame hits the broadband or LTE link. The router is just going to repackage everything into whatever frame size it agreed upon with the ISP's equipment or the cell tower, and you've got zero say in that process.

Sadly, I don't see any way to squeeze more performance out of this unless you've got full control over the router.
Check this out
I'm hitting a wall here—whenever I run ping -l 1434 google.com, I get hit with multiple timeouts in a row.

If I try ping -f -l 1434 google.com, I'm seeing 3 losses on one go, and then 4 losses for the next 5 attempts.

But if I drop it down to ping -f -l 1432 google.com, everything works perfectly fine.

That right there? That's where your packets are getting shredded. You're basically hitting a ceiling between 1432 and 1434 bytes for the IP packet size at Layer 3. Just remember, the actual Layer 2 frame is always going to be a bit beefier because of all that extra IP overhead.

And honestly, Google.com doesn't matter here—it’s not affecting your actual performance. These jumbo frame limitations usually pop up on local networks since you're running on an Ethernet setup. A frame size can't just sail right through a router if it's too big.

Try using a ping with the -f flag to hunt down the absolute max IP packet size you can push to your specific game server.

Also, do some digging to find the average packet size your game app is actually spitting out. It’s probably buried in one of those endless readme.txt files that nobody ever bothers to read.
Honestly, a simple ping has saved my skin a few times. I was mentioning before that you can actually crank up the IP packet size in a ping up to 64k, which lets you mess around with IP packet fragmentation at Layer 3—and that’s directly tied to how big the Layer 2 frames are.

Size = l (length)

Try to hunt down the IP address for a standard gaming server or even a streaming server. Once you have it, start pinging them using non-default sizes to see what happens to your round-trip time. Watch how things change when you bump the packet size from the standard 32 bytes all the way up to the 64k limit.

Here’s an example:
default;
ping -l 32 (IP address)

ping -l 64

ping -l 128, and just keep going until you hit 65535.

The network starts behaving totally differently once you cross certain thresholds. It really comes down to those "jumbo frames"—basically Ethernet frames that are bigger than the usual 1512-byte max. People use larger frames for things like streaming or heavy email traffic because there's way less overhead involved.

Also, try running a ping test where you tell it *not* to fragment anything. IP packets get "broken up" for all sorts of reasons, usually because different links along the path don't agree on the frame size. If you're using GRE, it gets even messier because those fragmented packets have to be resequenced back into their original order. I’ve dealt with situations where the end-to-end ping size was barely hitting 500 bytes. Once I finally got my ISP to align their links properly, everything smoothed out massively.

To disable fragmentation:

ping -f

Example for a standard Ethernet packet:

ping -f -l 1512 (IP address)

If the ping tells you it can't go through, then boom—you've found a fragmentation issue.

When you're gaming, the secret sauce is knowing the default IP packet size for that specific game or server so you can optimize the end-to-end transfer. Every single time a packet gets "split," you're looking at extra latency.